Cyber attacks and data breaches are rarely out of the headlines for long.
From major businesses and public bodies to charities and their technology providers, recent incidents have shown just how quickly a cyber security issue can affect organisations and the people who trust them with their data.
While attacks on household names naturally attract attention, cyber security isn't only a concern for large organisations.
If your business relies on email, cloud platforms, customer data, connected devices, third-party software or digital systems, there is something worth protecting.
So, there's an important question every organisation should be asking:
How exposed would your business be if something went wrong?
Cyber security is becoming increasingly difficult to ignore
A recent incident involving a UK charity provides a timely example.
In August 2026, the BBC reported that Manchester-based HIV charity George House Trust had informed users that sensitive and personal health information may have been stolen following a data breach.
According to the charity, information downloaded by hackers potentially included addresses, email addresses, telephone numbers and notes and records relating to people's engagement with the organisation. At the time of the report, there was no indication that the stolen information had been misused.
But there was another important part of the story.
The breach involved Beacon, a technology company providing a database system used by more than 1,000 charities. The wider cyber security incident could potentially affect as many as 1,500 charities across the UK, according to the BBC report.
That highlights an important reality of modern cyber security.
Your risk doesn't necessarily stop at your own network.
And it's not an isolated example
Just a day later, another major data breach was making headlines. In August 2026, Manchester Airports Group confirmed that information relating to around 8.7 million customers had been accessed following a cyber attack affecting systems used across Manchester, London Stansted and East Midlands airports.
According to reports in The Guardian, the compromised information included email addresses, telephone numbers, postcodes and vehicle registration details. The affected system did not contain payment or banking information, and airport operations and aviation security were not affected.
The two incidents are very different in scale and circumstances, but they reinforce the same point: organisations of all shapes and sizes can find themselves exposed, and the impact of a cyber incident can extend far beyond the organisation initially targeted.
Your suppliers can be part of your cyber risk
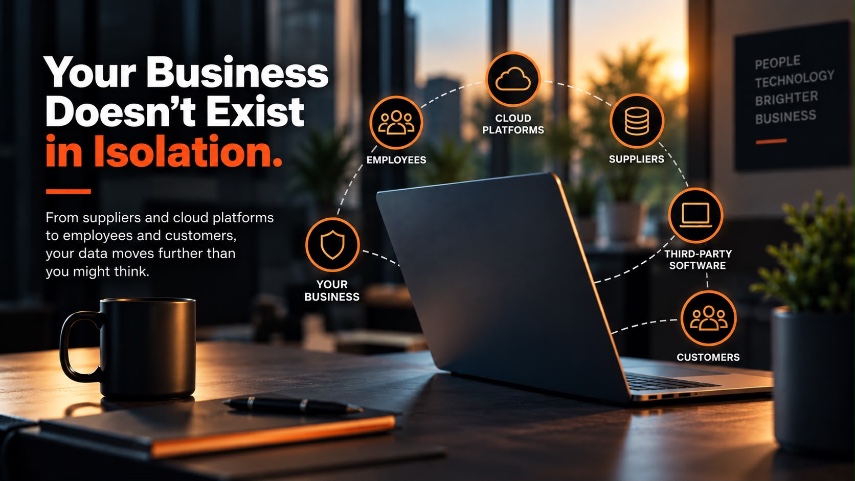
Modern businesses rarely operate entirely within their own IT environment.
Cloud services, CRM systems, payment providers, software platforms, outsourced IT services and other third parties can all store, process or have access to important information.
That brings enormous benefits, but it can also introduce another layer of risk.
The National Cyber Security Centre (NCSC), part of GCHQ and the UK's technical authority for cyber security, specifically warns organisations about cyber security risks arising from suppliers and other third parties.
Its guidance notes that supply chains can be large and complex, making it difficult for organisations to know whether they have sufficient protection in place. The NCSC also says there has been a significant increase in cyber attacks resulting from vulnerabilities within supply chains in recent years. (National Cyber Security Centre)
Its Cyber Assessment Framework goes further, advising organisations to understand what data is held by suppliers, manage third-party connections and make sure appropriate security requirements are in place when external services are used.
The lesson for businesses is straightforward: understanding your own security is essential, but so is understanding where your data goes and who else has access to it.
A data breach doesn't have to start with you
Think about how many external systems your business uses every day.
Your customer data might sit within a CRM. Files could be stored in the cloud. Your employees may access several third-party platforms. Suppliers could connect to your systems, while external providers may process or store information on your behalf.
The NCSC recommends maintaining visibility over third-party goods, services and suppliers and understanding who is responsible for their security.
For businesses, that means asking questions such as:
What data do our suppliers hold?
Who has access to our systems and information?
What security measures do our suppliers have in place?
What would happen to us if one of those suppliers suffered a cyber attack?
Would we know quickly if our information had been compromised?
These aren't questions designed to create fear. They're part of understanding your overall exposure and making informed decisions about where improvements may be needed.
The UK's approach to cyber resilience is changing too
All of this comes as the UK strengthens its approach to cyber security and resilience.
The Cyber Security and Resilience (Network and Information Systems) Bill was introduced to Parliament in November 2025 and is intended to update the existing Network and Information Systems Regulations.
Among the proposed changes are expanded protections for essential and digital services, new provisions covering areas including relevant managed service providers and data centres, and stronger requirements around the reporting of harmful cyber incidents.
For regulated organisations, the Bill proposes a two-stage reporting process for qualifying incidents. An initial notification would be required within 24 hours of becoming aware of an incident, followed by a fuller report within 72 hours. The NCSC would be informed alongside the relevant regulator.
Not every UK business will fall directly within the scope of the legislation.
But the direction is significant.
Cyber security is increasingly about more than attempting to prevent an attack. Organisations also need to think about resilience: understanding their risks, identifying incidents, limiting their impact and being prepared to recover.
How exposed is your business?
You don't need to wait for an incident to discover where weaknesses exist.
A good starting point is understanding the technology, processes and people your business currently relies upon and asking whether the appropriate protections are in place.
For example:
Are your systems up to date?
Software updates and security patches help address known vulnerabilities before they can be exploited.
Are your accounts properly protected?
Strong authentication and appropriate access controls can reduce the risk of compromised credentials leading to wider access.
Do you know where your data is stored?
Understanding which systems and suppliers hold sensitive business or customer information is an important part of managing risk.
Have you considered your suppliers?
The NCSC advises organisations to understand their supply chains and assess the cyber security risks associated with suppliers and partners.
Are your backups secure and recoverable?
Having backups is one thing. Knowing they can be successfully restored when they're actually needed is another.
Would you spot suspicious activity?
The sooner an incident is identified, the sooner action can be taken to understand and contain it.
Does your team know what to do?
Technology is only part of the picture. Employees should understand basic cyber security risks and know what to do if something doesn't look right.
Cyber security starts with knowing where you stand
No organisation can remove cyber risk entirely.
What businesses can do is understand where their vulnerabilities lie and take proportionate steps to reduce their exposure.
That starts with getting a clear picture of your current position.
At Kuiper, we've created a Cyber Security Assessment to help businesses do exactly that.
The assessment takes you through key areas of your current IT security, helping to highlight where you're already well protected and where there may be gaps worth reviewing.
It's not about scare tactics or unnecessary jargon.
It's about giving you a clearer understanding of your current security so you can make informed decisions about what comes next.
Would your business pass the test?
Know where you stand. Strengthen your security. Prepare for what's next.
Complete the Kuiper Digital Resilience Assessment to get a clearer picture of your current security and uncover areas that may need attention.
Once you've completed the assessment, the Kuiper team can talk you through your results and help you understand where improvements could be made.